Research
Executable assurance.
Governed AI as Runtime Infrastructure: A Unified Authority and Evidence Architecture for Regulated Agentic Systems. Ernest Chiweshe, August 2026 (v5).
The claim, precisely
"The result is not a claim of automatic regulatory compliance. It is a narrower and more useful engineering contribution: authority becomes executable, failure becomes visible, and every released decision can be traced to the evidence that permitted it."
Every finding is stated with its evidence and its falsification criteria. Synthesis, not invention: safety cases, tool qualification, capability tokens, signed attestations, default-deny policy engines — composed into one per-decision executable enforcement path.
The paper (v5)
Abstract, related work and capability matrix, architecture, implementation, evaluation (adversary model, ten-domain replication, ten fault-injection drills, independent DSSE verification, real KMS/CloudHSM measurement), boundary. Available on request until the public copy is published. research/paper/paper.md
Evidence
Implemented. Operationally measured. Next to validate.
Implemented
- One authority path exercised across ten regulatory philosophies
- Consequence-aware, deny-by-default decisions
- Qualification records bound by digest
- Credentialed human approval
- Output-bound, single-use permits
- Signed evidence and write-once retention
- DSSE attestations verified by independent tooling securesystemslib 1.4.0
Operationally measured
- Real AWS KMS (Ed25519) and single-tenant CloudHSM (ECDSA P-384, FIPS 140-3 L3) signing profiles
- Retention on S3 Object Lock
- Sustained 24-hour governed execution: 854,100 decisions, 2,847 batches, zero failed batches
- Fail-closed against real outages: WORM permission revoked; HSM path severed release refused before any byte; chain intact
- Custody restored from backup in 372 s
Next to validate
- Authoritative identity-provider and licence-registry integrations deterministic local adapters today
- Calibrated probabilistic verifiers rule-based checkers today
- Regulator-approved qualification datasets
- Distributed fault injection; key-rotation overlap
- Independently authored domain packs
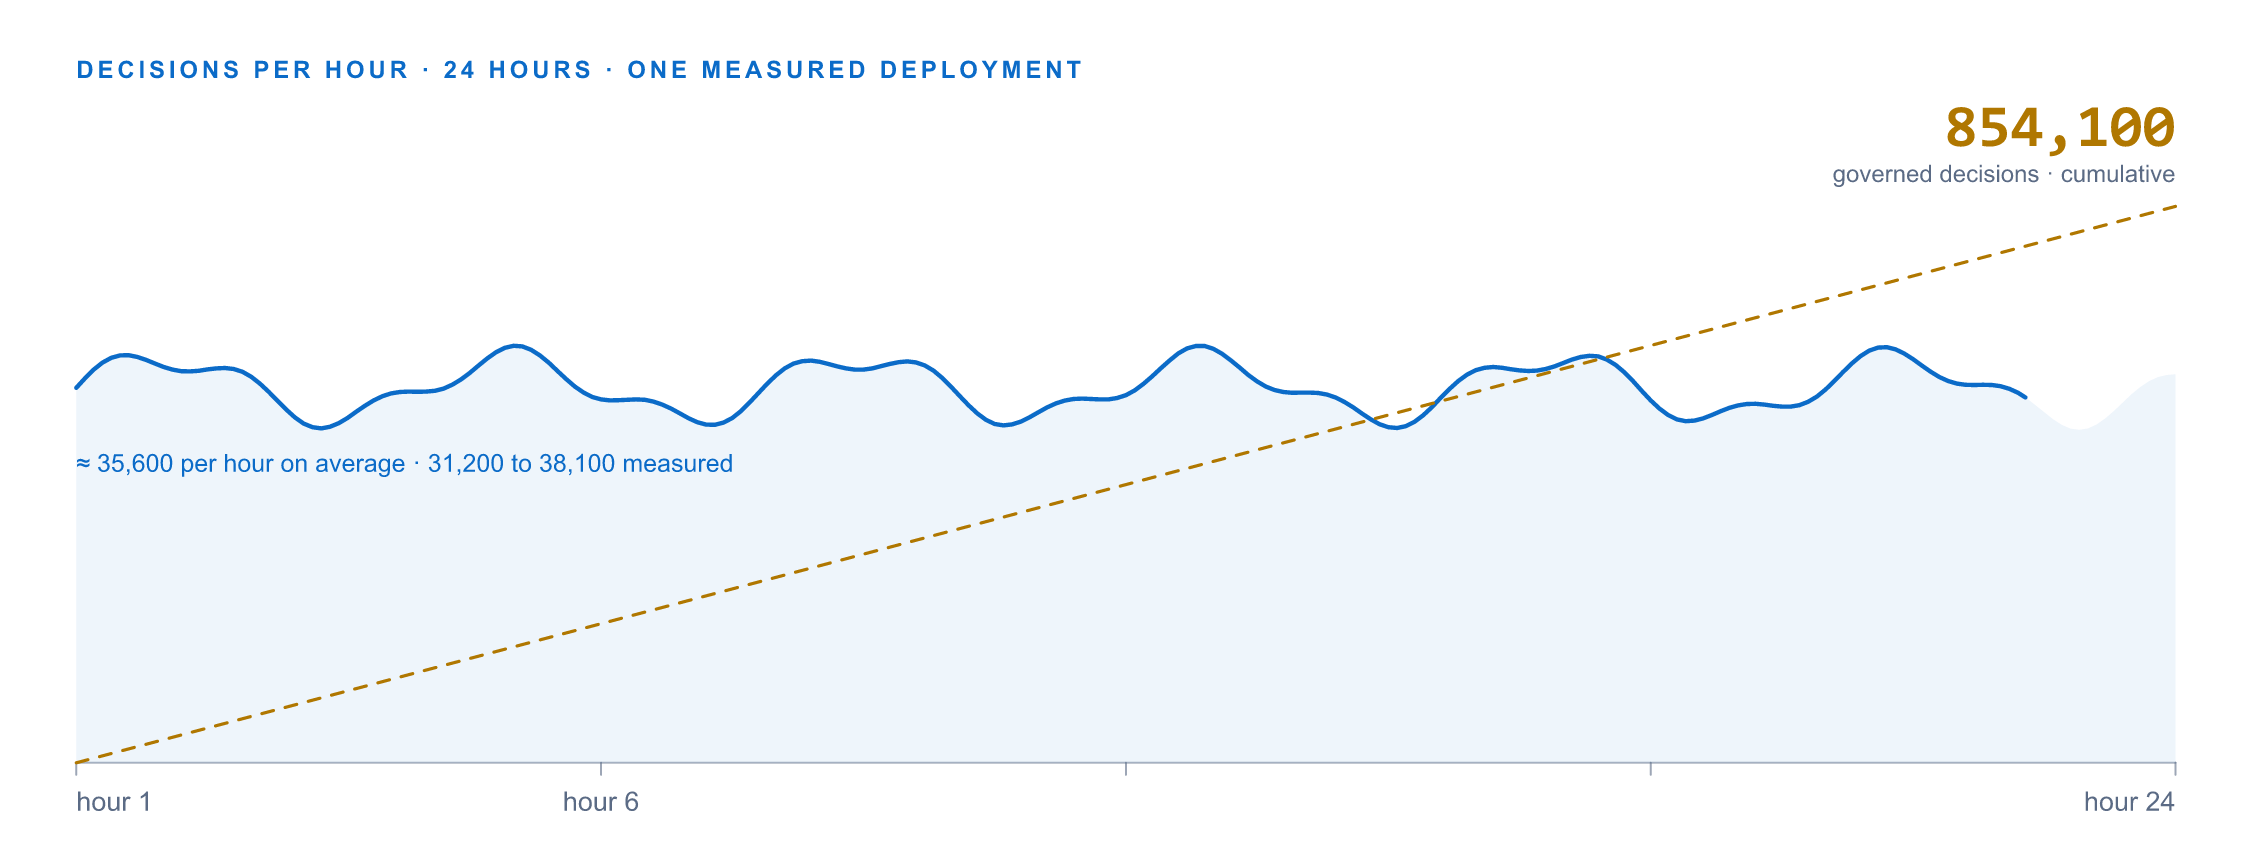
From the paper Governed AI as Runtime Infrastructure (August 2026).
What is not claimed
Identity-provider and licence-registry integrations use deterministic local adapters today. Verifiers are deterministic rule-based checkers. Qualification datasets are illustrative. The ten domains are proof packs, not products. Not validated as a certified production deployment. Conformity assessment and the management system remain institutional responsibilities.
Where the evidence goes next
Real identity-provider and licence-registry integrations, calibrated probabilistic checkers, and domain packs authored by independent teams: the strongest test of the platform is what others build on it.